#2fa
31 posts · Last used 18h
two interesting geeky things
https://nonfunctional.substack.com/p/passkeys-are-a-trap-do-not-use-them
https://royfish.dev/fingerprints-are-the-new-cookies
#OnlineSecurity #OnlinePrivacy #passwords #TOTP #2FA #passkeys #fingerprinting
TIL: KeePassXC has built-in support for TOTP code generation. How have I never discovered this in all the years I have been using KeePassXC??
cc: @keepassxc@fosstodon.org#security #software #keepassxc #totp #mfa #2fa
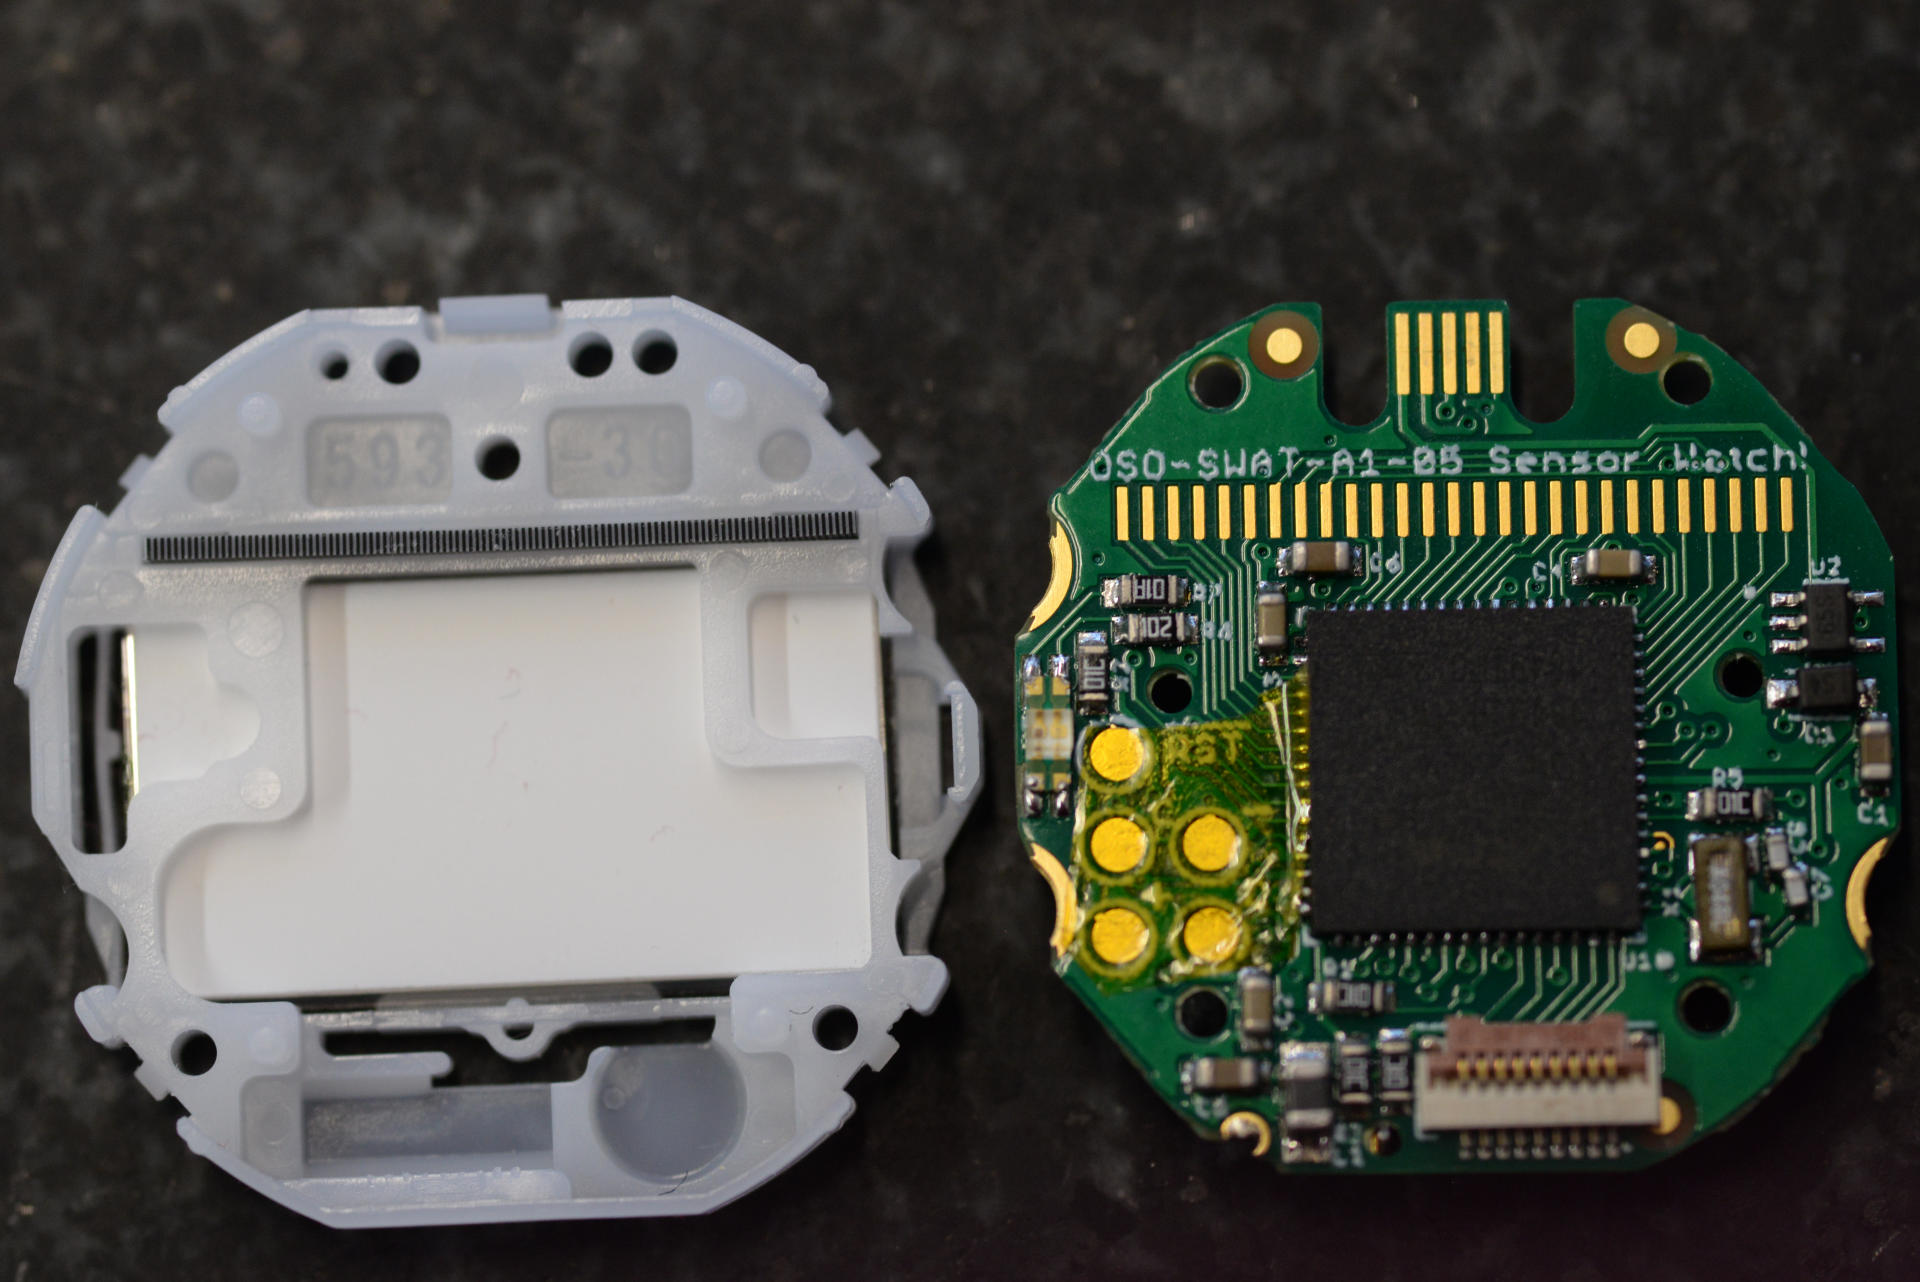
Did I mention, that #SensorWatchPro is pretty cool? With the totp_lfs_face #complication, I now have #TOTP #2FA on my #wristWatch, and it's not even a #smartwatch.
https://www.sensorwatch.net/
Thanks, @joeycastillo@mastodon.social!
(I use it only for non-critical logins, because access to the secrets is too easy with physical access to the device. E.g. NOT for #salsa #debian org.)
Replying to
Not only is Center for Internet Security, Inc. (CIS) still sending these, but they still have no multi-factor authentication for accounts.
From https://www.cisecurity.org/about-us
The CIS Vision
Leading the global community to secure our ever-changing connected world.
The CIS Mission
Our mission is to make the connected world a safer place by developing, validating, and
promoting timely best practice solutions that help people, businesses, and governments
protect themselves against pervasive cyber threats.
https://www.youtube.com/watch?v=51gf648nRyE&t=118s
#Phishing #ComplianceVsSecurity #CIS #CenterForInternetSecurity #MFA #2FA #InfoSec #InformationSecurity #CyberSecurity
Terminator 3: T-850 Corrupted
Replying to
While it may have taken them a moment, with the new CIS Portal for CIS Workbench, they have announced that,
"When your account is ready, you'll be guided through a brief process to choose a primary verification method, .."
Hardware tokens and/or passkeys, right?
"..like SMS ..."
When your account is updated, be sure to visit the Portal for
"CIS-curated thought leadership and cybersecurity resources to help you put best practices into action"
#Phishing #ComplianceVsSecurity #CIS #CenterForInternetSecurity #MFA #2FA #InfoSec #InformationSecurity #CyberSecurity
Replying to
@Sheep_Overboard@infosec.exchange https://my.gov.au/en/myaccount/settings/sign-in-settings#/ --- iirc within here is where you can change your #2FA arrangement, including to #TOTP
this is what i see now each time i login; it's really cool & works well
NB: you can use KPXC independent of your browser, but best optimisation arises when using it with the official KPXC addon in one's browser, as i learned to do.
If you make your employees install your 2FA onto their personal devices then you should expect them to check all the notifications and updates and scroll all the conversations in all apps in the devices every time they (re)login into your system.
#productivity #security #wfh #office #totp #2fa #authenticator
I noticed that signing in to Mastodon using 2FA didn't reliably work. Turns out my system clock was ~30 seconds behind that of the actual time (currently GMT +1 for me).
On Linux distributions that have systemd, systemd apparently synchronises your system time with a time server automatically. However, I use Devuan (i.e. Debian but without systemd) so I had to do it manually.
I used htpdate to set the time to a UK time server on pool.ntp.org like this:
sudo htpdate uk.pool.ntp.org
No need to reboot. It's now accurate to GMT+1 to within about half a second. :)
Hashtags: #Devuan #time #system #Linux #2FA #systemd #Debian
my:
bankcredit card ex company1credit card ex company2superannuationmobile phone vendornbn broadband vendor
do not use / support #2FA via #MFA #TOTP, & i am tearing my hair out in exasperation at these damn troglodytes. I've even just wasted a coupla hours dealing with my mobile phone vendor who overnight sent out an email that delighted me as it recommended customers setting up our online accounts with them using [direct quote from the fucken email]...
MFA is a security method that requires you to prove your identity in two or more different ways, like an additional verification step as part of your login. This might include facial recognition, a dedicated authenticator app, or a unique code sent to your preferred contact method.
...only to eventually find that part of the email is bullshit.
jfc, most of these are major companies, some indeed are multi-nationals, yet they still treat security as a joke. utter fuckheads!
aaaaaaand yet seemingly not a week goes by without companies getting hacked & thus fucking over their customers 😡🖕
Replying to
@Mae@is.badat.dev so can I finally mandate PGP-based 2FA (like on dread)?
Cuz I won't install a garbage app that won't run on my devices anyway and I won't have TOTP / HOTP available all the time…
#PGO #2FA #App #Enshittification #OTP #TOTP #HOTP
Die neue #TOTP Funktion in #ruccuDB 0.0.3 wirkt für eine Daten Engine auf den ersten Blick vielleicht ungewöhnlich.
Gerade darin liegt aber ihr Vorteil: TOTP Secrets werden nahtlos in der Engine verwaltet und verschlüsselt gespeichert. Anwendungen, Plugins oder andere Konsumenten können dadurch ohne eigene Kryptografie eine #2fa Lösung auf Basis von RuccuDB in PHP integrieren.
#dev #coding #development
Replying to
CVE-2025-0679 named them. NVD and MITRE still can't agree on whether you had a fighting chance. You did not.
Update your Zimbra webmail client to the patched version immediately, or TA488 keeps the loot.
Reward: You've received a hollow Authenticator Token — pre-drained.
#ZeroDay #Zimbra #Espionage #CyberSecurity #2FA #AchievementUnlocked (2/2)
Replying to
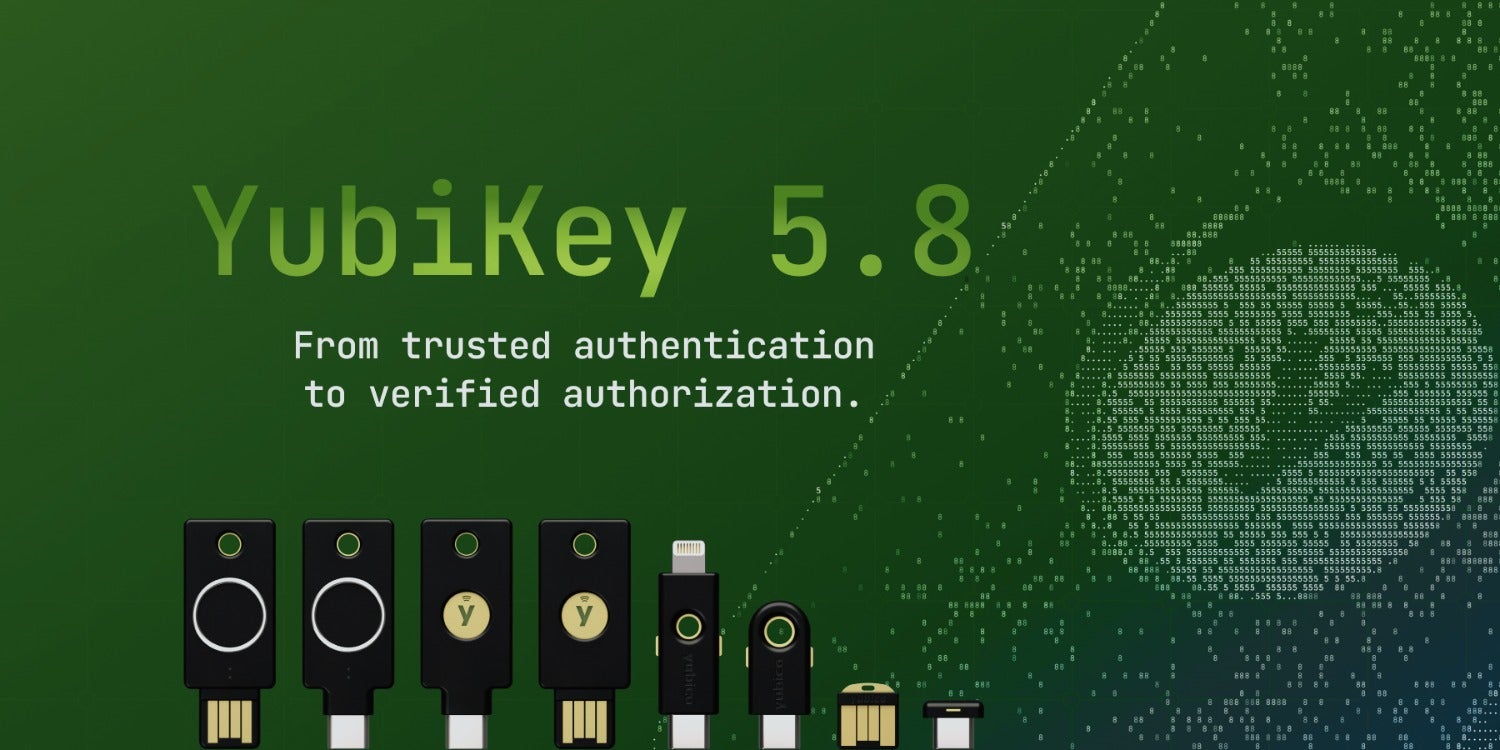
@tychotithonus@infosec.exchange speaking of Yubico, it looks like they finally released firmware 5.8. I'm not sure how I feel about all of the GenAI "features" they added.
https://www.yubico.com/blog/beyond-the-login-top-3-things-developers-need-to-know-about-yubikey-5-8/
#Yubico #Yubikey #CTAP #2FA #SecurityKey
@disroot@nixnet.social @disroot@social.weho.st hello, can you pls tell me if #disroot #webmail login can be protected by using #2FA #TOTP?
CVE-2026-62232 (CRITICAL): getgrav Grav <2.0.4 has a 2FA bypass flaw — attackers knowing a user's password can overwrite the 2FA secret, reducing protection to password-only. Monitor & restrict access. Patch status pending. https://radar.offseq.com/threat/cve-2026-62232-missing-authorization-in-getgrav-gr-604d58721f0c378d #OffSeq #CVE202662232 #2FA #infosec
@jerry@infosec.exchange hi Jerry. i vaguely recall a post of yours from several weeks / maybe some months? ago, where you said you were going to introduce mandatory #TOTP / #2FA for accounts. that alarmed me coz i do not have any TOTP facility atm, & tbh know nothing about this tech at all. as i largely use #sharkey rather than masto for my daily fediversing these days, i shoved this into the too hard basket, & forgot about it.
today though i chanced across discovering that my long-term password manager, #keepassxc, also includes a TOTP capability. i've now begun investigating it, though atm i still don't really understand it. this reminded me of that recent? post of yours, so i thought maybe i'd use my masto account for my first TOTP guinea pig. i fell at the first hurdle. the masto settings section for 2FA says: Two-factor Auth
If you enable two-factor authentication using an authenticator app, logging in will require you to be in possession of your phone, which will generate tokens for you to enter.i do not use my phone for anything other than calls + sms. i have no intention to change from using my linux pc for my fediversing & all other interwebzing, to my phone. does this mean then that my infosec.space account is doomed? eg, next time i log out, for whatever reason, i'll no longer be able to log back in, if you have activated mandatory 2FA, & i don't have it?
i'd really hoped that belatedly discovering kpxc [on my linux desktop] has totp might be my solution, but now i'm only more confused. thx.
What's your favourite authenticator app?
#2FA #OpenSource #authenticator #apps #EULogin #MicrosoftAuthenticator #Google #Microsoft
What's your favourite authenticator app? #2FA #OpenSource #authenticator #apps #EULogin #MicrosoftAuthenticator #Google #Microsoft
This is the warning message I get for the MFA 2FA multi-factor authentication parameters for the freeBSD forum.
Is there anyone here who can tell me where I can post this so that they can look into the issue?
@stefano@mastodon.bsd.cafe
Please boost for visibility
#freeBSD #BSD #MFA #2FA #InfoSec #weak #cryptography #cipher #programming #OpenSource #forum