Remote
buherator
@buherator@infosec.place
akkoma 3.20.1-8-g80084427-main
"I'm interested in all kinds of astronomy."
1661 Followers
742 Following
50 Posts
Replying to
@HennaVirkkunen@ec.social-network.europa.eu You are an idiot.
Open post
[RSS] Advisory X41-2026-004: dm-verity can be bypassed in Debian live-boot
https://x41-dsec.de/lab/advisories/x41-2026-004-debian-live-boot/
0
0
0
0
Open post
Replying to
@jerry@infosec.exchange It *is* timeline dependent! I had to scroll back more than a day (I stupidly overwritten the original screenshot with the crop, but the timestamp helped).
So far I could get this out from some vibe coded event handler in dev tools:
"Local Network Access permission required: top-level site “https://infosec.place/” initiator “https://infosec.place/” attempting to access target “http://localhost:3000/assets/images/og-card.png” (127.0.0.1:3000) via http. Secure context: True"
0
16
0
0
Open post
I thought I'm making up a conspiracy theory around NVIDIA architecting the AI bubble after the crypto bubble bursted. It seems @david_chisnall@infosec.exchange agrees (sort of):
RE: https://infosec.exchange/@david_chisnall/117075838205635406
Open quoted post
Quoting
@MiaMarkTwo@syzito.xyz @statsguy@mas.to
NVIDIA has a speedrun of the problem that a lot of companies had.
They started making a fairly niche product: a 3D accelerator for gaming. This was something that was a fairly limited (but high margin) market. They were able to take a lot of the graphics workstation market because their products were not quite as good but a lot cheaper than existing players there, but that had always been a tiny market.
They were lucky because the costs were coming down and the time that they entered the market was about the time it was possible to create something that was just about cheap enough to go from the gamer market that 3dfx targeted to the wider every-computer-needs-one market.
That gave them a load of early growth. The market likes growth.
Then they released programmable shaders and the entire GPGPU movement started. That let them sell parallel compute engines that operated on regular data to a load of places that didn't care about graphics. Not the highest volume, but a larger market than 3D workstations ever were and similar margins.
That gave them more growth. The market likes growth.
When they were starting to reach market saturation, they released cards that were good at cryptocurrency 'mining'. Suddenly there was a path that let people buy NVIDIA GPUs and use them to create money (or, at least, things people were willing to exchange for money).
And that gave them more growth, albeit driven by an obvious bubble. The market likes growth.
But that bubble was going to burst. Augmented reality looked like a possible replacement but the people in that space were mostly building their own low-power chips (and it failed to take off). They needed a new bubble. Fortunately, someone combined the knowledge that you could represent layers in feed-forward neural networks as matrixes and then run them very quickly on a machine that was good at doing independent floating-point operations over regular data structures. And so you could run large feed-forward neural networks on GPUs. Bubble opportunity! So they hyped the hell out of that new use case.
And that led to a load of new orders. And that's growth! The market likes growth.
Unfortunately, none of their customers were actually making money from the GPUs used for running these neural networks. Unlike the previous bubble (where people were making money, though mostly from things that looked a lot like scams), this one needed to be fuelled by throwing more capital in. So they started doing all sorts of exciting deals with this kind of structure:
NVIDIA invests in a company, marking it down as capital expenditure.
The company turns around and promises to spend all of the money on NVIDIA GPUs.NVIDIA reports that money as revenue.The market sees increased revenue and knows that the value of a company is some multiple of its revenue, so the value of NVDA increases by more than the cost of the initial investment.NVIDIA sells enough shares to cover the investment.
Apparently this is legal, but it absolutely shouldn't be. But each new investment loop like this generates more customers, which signals growth, and the market loves growth.
The systemic problem is that the stock market redirects capital to things that have the potential for growth and this gives a huge incentive for any company to demonstrate growth. A company that has saturated its market and is consistently producing good products is less attractive to investors than one that is in a growing area. If you are in a market that is saturated, you need to either keep entering new markets (which, again, should be triggering antitrust laws because cross subsidies are illegal and about the only way you can successfully do this) or provide some rationale to the stock market of why your saturated market can grow.
But I don't think that absolves NVIDIA. They have been doing a lot of deeply unethical things and I hope a future SEC (or European regulators, once they realise Trump's SEC is a waste of space) will determine that they were illegal. And I will absolutely remember the people who were celebrating Huang while he was doing all of this.
Open quoted post 0
1
0
0
Open post
Seems like AI companies are not that easygoing when they are on the wrong end of hacking :P
https://threadreaderapp.com/thread/2101252692635004997.html
0
0
0
0
Open post
[RSS] LLMs won't break symmetric crypto
https://www.bfswa.blog/p/llms-wont-break-symmetric-crypto
0
0
0
0
Open post
Open post
[RSS] KindaRails2Shell: arbitrary file read to RCE in Rails Active Storage via libvips (CVE-2026-66066)
https://ethiack.com/info-hub/research/kindarails2shell-rails-rce-cve-2026-66066
0
0
0
0
Open post
Open post
Open post
[RSS] Is This A Joke? In The Auth Header? (F5 BIG-IP UnAuth Heap-Overflow to RCE CVE-2026-94127)
https://labs.watchtowr.com/is-this-a-joke-in-the-auth-header-f5-big-ip-unauth-heap-overflow-to-rce-cve-2026-94127/
0
1
0
0
Open post
Replying to
@VoltPaperScissors@chaos.social @inselchaos@chaos.social This looks amazing! Does the multi-rotor part actually work??
0
4
0
0
Open post
Open post
[RSS] Chamilo LMS... It's raining 0days, hallelujah, it's raining 0days
http://blog.quarkslab.com/chamilo-lms-its-raining-0days-hallelujah-its-raining-0days.html
0
0
0
0
Open post
This IT Crowd episode predicted the AI boom (except instead of covering bad team dynamics we try to prevent $NVDA go down):
https://www.youtube.com/watch?v=uyV0IVItlM4
The it crowd - Denholm Hello Computer
0
0
0
0
Open post
[RSS] Apple Reference Image: A New Approach for Verified Photography
https://security.apple.com/blog/apple-reference-image
0
0
0
0
Open post
Replying to
@VoltPaperScissors@chaos.social @inselchaos@chaos.social Still very cool, Pocket Encrypt already looks like a spy gadget (IMO that's really important when teaching cryptography :))!
0
1
0
0
Open post
[RSS] The Binary Hiding in Your Registry: Cracking Windows UCPD's Dynamic Rules
https://binary.ninja/2026/08/04/ucpd-dynamic-rules.html
0
0
0
0
Open post
FFS Reddit is now using "protecting communities from scrapers" as an excuse to kill RSS.
Great job everyone coming up with this BS!
https://old.reddit.com/r/modnews/comments/1tq9vxo/protecting_communities_from_scrapers_and_platform/
0
1
0
0
Open post
Open post
I recently learned to distinguish rabbits from hares (from a shitpost ofc) and now I feel slightly offended because my emoji keyboard shows a rabbit but it clearly renders as a hare in the app. 🐇
0
0
0
0
Open post
[RSS] CVE-2026-43783: Repair Permissions - Get Root: LPE via DesktopServicesHelper in macOS 26.5
https://ptswarm.com/blog/cve-2026-43783-repair-permissions-get-root-lpe-via-desktopserviceshelper-in-macos-26-5/
0
0
0
0
Open post
Open post
Session timeouts[1] provide great examples of #compliance disconnects from reality:
When booking for events it *always* takes *days* to get from registering for an event and getting there to show your QR or whatever. And while an attacker who hijacks your session has 0 benefit from accessing it for a prolonged time, somehow #security finds it crucial that users are auto logged-out after 30mins.
It would take just a *tiny* bit of thinking to avoid making things worse for everyone.
[1] https://wstg.owasp.org/latest/4-Web_Application_Security_Testing/06-Session_Management/07-Session_Timeout/ (congrats to #OWASP for breaking all your indexed links in search engines, also very helpful!)
0
0
0
0
Open post
Replying to
@jerry@infosec.exchange @dey@mastodon.social I can see the Initiator is an img, but I can't find anything seemingly related in inspector + network rectord don't tell me what code initiated a request. That's the status.
0
2
0
0
Open post
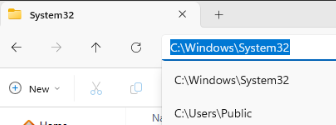
That's right, the right answer for this questions is: 3!
By first pressing the down arrow you remove the selection (which you didn't put there) from the address bar text. The two downs are needed to reach C:\Users\Public.
"2 or 3" would be also acceptable, because if you don't just click the address bar, but start to type in it, there is no selection to remove.
https://infosec.place/objects/85dfac07-d1d6-412b-832c-897be5be860b
Open quoted post
Open quoted post
Quoting
#Windows experts, can you answer this without trying:
How many times do you need to press the down arrow to select C:\Users\Public?
#UX #UI

0
0
0
0
Open post
"This 3-day training focuses on macOS Vulnerability Research (VR) for beginner to intermediate students. While intermediate topics will be discussed, the course focuses on bringing security researchers up to speed with macOS’s unique protections and vulnerabilities"
Great content from my friends, now in Budapest:
https://macosvuln.training
Great content from my friends, now in Budapest:
https://macosvuln.training
0
0
0
0
Open post
Replying to
@codinghorror@infosec.exchange CEOs often work for minimal wage for tax reasons around here. But even that case is much better than simply asking your billionaire friends to push literal peanuts your way along with a job contract 2 years before you run for office.
0
4
0
0
Open post
[RSS] 22 CVEs in TeamDavid(R) a "secure" M365 alternative
https://labs.infoguard.ch/posts/22-cves-in-david-a-secure-m365-alternative/
0
0
0
0
Open post
Replying to
If you like this post, please consider supporting this GitHub issue:
https://github.com/rust-lang/cargo/issues/16574
#Rust #Cargo
0
0
0
0
Open post
Replying to
@dey@mastodon.social The cybersecurity awareness you spread to me starts to itch. It also hurts to pee.
@briankrebs@infosec.exchange
0
0
0
0
Open post
Replying to
@dey@mastodon.social @jerry@infosec.exchange More details pls, who is trying to figure out if I have SW X installed and how?
0
10
0
0
Open post
[RSS] XProtectRemediatorDubRobber infoleak on macOS (CVE-2024-40842)
https://gergelykalman.com/CVE-2024-40842-xprotectremediatordubrobber-infoleak-on-macos.html
0
0
0
0
Open post
[RSS] Escaping Linux Sandboxes via PipeWire (CVE-2026-5674)
https://embracethered.com/blog/posts/2026/pipewire-flatpak-linux-sandbox-escape-cve-2026-5674/
0
0
0
0
Open post
Replying to
@VoltPaperScissors@chaos.social @inselchaos@chaos.social Pringles Enigma! Brilliant! Although as I understand the Enigma part is not delivering electricity (yet)?
0
2
0
0
Open post
An old friend is ashamed of speaking English with people but want to practice. Any pro/cons of using an educational chatbot for this?
At first I find this a pretty good use case for language models.
0
3
0
0
Open post
Replying to
@dey@mastodon.social @jerry@infosec.exchange But I'm not using Mastodon, this is an Akkoma instance. And this only happens if I scroll back to the point in my timeline when I first got this notif. It'd be really weird if this behavior didn't trigger at around page load.
0
8
0
0
Open post
[RSS] What Go Taught Us About Java Garbage Collection
https://debugagent.com/what-go-taught-us-about-java-garbage-collection
0
0
0
0
Open post
Open post
Replying to
@jerry@infosec.exchange Based on this article and the previous error I assume this permission request is not coming from JS but someone trying to make me fetch an URL from localhost which now triggers additional warnings:
https://support.mozilla.org/en-US/kb/control-personal-device-local-network-permissions-firefox
At this point I'm not sure if it should be illegal for posts to contain references to localhost.
0
0
0
0
Open post
When you help out at a friends kitchen and take a nice looking knife they're usually like "it's shit, don't use that! use this." then hand you an old piece in seemingly questionable condition that was used to skin bears during The War and is still so sharp you need safety goggles just to look at it.
Is this world-wide or just an Eastern-European thing?
#cooking
0
2
0
0
Open post
Replying to
@jerry@infosec.exchange Original timestamp of the image:
Wed Sep 23 09:14:13 PM CEST 2026
It's the first time I see such request ever (not just here).
0
20
0
0
Open post
Replying to
@tychotithonus@infosec.exchange I miss OS diversity too, guess it'll be a future improvement? Prioritizing Linux instructions makes sense if you consider CI pipelines.
0
0
0
0
Open post